H.R. 3259: Post Quantum Cybersecurity Standards Act
Sponsor
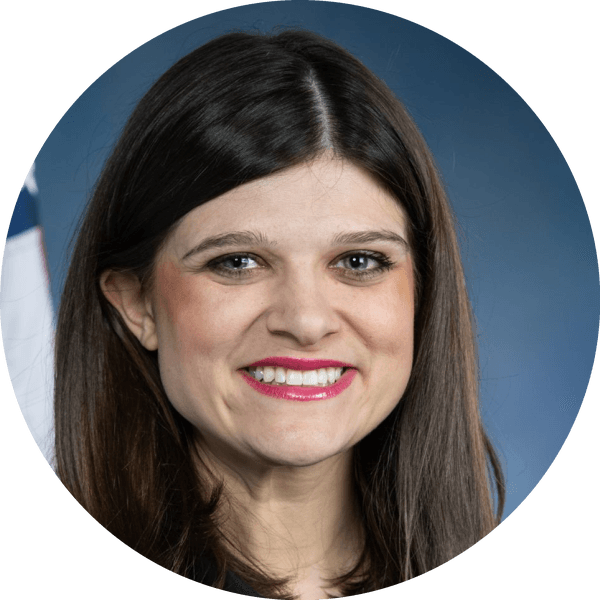
Haley Stevens
Democrat · MI-11
Lock down the grid and hospitals before quantum codebreakers arrive
Why it matters
The encryption guarding your bank login, medical records, and the power grid could one day be broken by a large enough quantum computer. H.R. 3259 cleared the House Science Committee 35-0 and would make NIST responsible for helping the most exposed operators switch to quantum-resistant encryption, with grants possible once Congress funds them.
Most encryption in use today rests on math problems that ordinary computers can't solve in any useful amount of time. A large-scale quantum computer could solve some of them, which is why cryptographers have spent years building replacement methods known as post-quantum cryptography. The bill defines it simply: encryption assessed not to be specifically vulnerable to attack by either a quantum or a classical computer.
H.R. 3259 makes NIST responsible for getting that new encryption into the systems Americans rely on, starting with the ones most likely to be targeted. Working with the Department of Homeland Security and the federal agencies that oversee each critical sector, NIST would publish free guidance and resources for any organization making the switch. It would also offer hands-on technical help, where practicable, to high-risk operators such as critical infrastructure and digital infrastructure providers.
Nothing here is mandatory. No company is ordered to replace its encryption, and there are no deadlines, fines, or penalties — adoption stays voluntary.
The bill also sets up a possible grant program, with two strings attached: Congress has to appropriate money, and NIST has to have issued post-quantum standards first. If both happen, high-risk entities could get grants covering reasonable costs of upgrading and fixing quantum-related weak spots, up to a cap NIST sets. The bill names no dollar figure, leaving eligibility, grant size, and duration to NIST.
Finally, it adds post-quantum cryptography by name to the National Science Foundation's federal cybersecurity research agenda, pairing near-term deployment help with longer-term research.
Bill Progress
Latest Action · Jun 11, 2025
Committee approved bill for floor consideration by the Yeas and Nays: 35 - 0.
H.R. 3259 Bill Summary
What H.R. 3259 actually does.
Free guidance for any organization making the switch
NIST must publish and share guidance and resources to help organizations adopt and deploy post-quantum encryption standards, consulting with Homeland Security and the federal agencies that oversee critical sectors.
Hands-on help for the most exposed operators
NIST must provide technical assistance, where practicable, to entities at high risk of quantum codebreaking attacks, such as critical infrastructure and digital infrastructure providers.
Upgrade grants, once Congress pays for them
NIST may create a grant program for high-risk entities, but only if Congress appropriates funds and only after NIST has issued post-quantum standards. Grants would help cover the cost of adopting the standards and fixing quantum-related vulnerabilities.
NIST sets the grant size and rules
The bill sets no dollar figure. Grants cover reasonable costs up to an amount NIST establishes, and NIST may write and update rules on eligibility, application requirements, grant size, and duration.
Industry and nonprofits get a seat at the table
If the grant program launches, NIST must consult CISA, other sector agencies, and private-sector representatives, including nonprofits, to share information about the program and its guidance.
Post-quantum research becomes a named NSF priority
The National Science Foundation's federal cybersecurity research agenda would explicitly include post-quantum cryptography.
Plain definitions written into law
The bill defines post-quantum cryptography, critical infrastructure, and sector risk management agency, so it's clear what counts and who is covered.
Who benefits from H.R. 3259?
Utilities, hospitals, water systems, and other critical infrastructure
The operators whose failure would ripple into daily life could get direct technical help from NIST and, if funded, grants to offset the cost of upgrading their encryption.
Internet and cloud providers
Digital infrastructure providers are named as high-risk entities, putting them first in line for targeted guidance, technical assistance, and potential grants.
Anyone whose data sits on those systems
Your financial, health, and account records are only as safe as the encryption protecting them. Earlier upgrades shrink the window in which data captured today could be decrypted later.
Cryptography researchers
Researchers funded by the National Science Foundation gain an explicit federal mandate for post-quantum work, making it a named research priority rather than an implied one.
Who is affected by H.R. 3259?
NIST
Takes on a new statutory job: promoting adoption, publishing guidance, assisting high-risk entities, and potentially designing and running a grant program — likely without new money unless appropriators provide it.
Department of Homeland Security and CISA
DHS must be consulted on the deployment effort, and CISA's director must be consulted on the grant program if it is created.
Sector risk management agencies
The federal agencies that oversee specific sectors, such as energy or health, are drawn into the deployment effort and grant consultations.
Private companies and nonprofits
Face no mandate or penalty. Some may qualify for help as high-risk entities; others may be consulted as the grant program takes shape.
HR3259 Legislative Journey
House: Vote: 35-0
Jun 11, 2025
Ordered to be Reported by the Yeas and Nays: 35 - 0.
House: Committee Action
May 7, 2025
Referred to the House Committee on Science, Space, and Technology.
About the Sponsor
Haley Stevens
Democrat, Michigan's 11th congressional district · 7 years in Congress
Committees: Science, Space, and Technology, House Select Committee on the Strategic Competition Between the United States and the Chinese Communist Party, Education and Workforce
View full profile →
Cosponsors (3)
All 3 cosponsors are Republicans. Cosponsors represent 3 states: Iowa, New York, Pennsylvania.
Committee Sponsors
Science, Space, and Technology Committee
1 of 40 committee members cosponsored

18 Democrats across this committee haven't cosponsored yet. Mobilize their constituents
What laws does H.R. 3259 change?
1 changes
Sections Amended
Section 4 of Cyber Security Research and Development Act (15 U.S.C. 7403)
inserting ``, including post-quantum cryptography'' before the semicolon
H.R. 3259 Quick Facts

- Committee
- Science, Space, and Technology
- Chamber
- House
- Policy
- Science, Technology, Communications
- Introduced
- May 7, 2025
Committee approved bill for floor consideration by the Yeas and Nays: 35 - 0.
Jun 11, 2025
Official Sources
Official bill record with full text, sponsors, and the House Science Committee's 35-0 markup vote.
The Congressional Budget Office's estimate of what the bill's technical assistance and grant program would cost if funded.
The NIST program that develops the post-quantum standards this bill would have NIST help high-risk organizations adopt.
The August 2024 standards whose issuance is a precondition for the bill's grant program.
CISA's effort to move critical infrastructure to post-quantum encryption; the bill requires NIST to consult CISA on its grant program.
Joint federal factsheet on the inventory and roadmap steps organizations take before switching to quantum-resistant encryption.
The 16 sectors, from energy to healthcare to water, that make up the critical infrastructure the bill treats as high risk.
The section of law the bill amends to add definitions of post-quantum cryptography, critical infrastructure, and sector risk management agency.
Who is lobbying on H.R. 3259?
3 organizations lobbying on this bill
QUANTUM INDUSTRY COALITION | 5 |
SB TECHNOLOGY, INC. D/B/A SANDBOXAQ | 2 |
MERLIN INTERNATIONAL, INC. | 1 |
Showing 1-3 of 3 organizations
H.R. 3259 Common Questions
What is post-quantum cryptography?
It's encryption designed to hold up against quantum computers as well as ordinary ones. H.R. 3259 defines it as methods assessed not to be specifically vulnerable to attack by either kind of computer.
Does H.R. 3259 force companies to change their encryption?
No. NIST is told to promote voluntary adoption. There are no deadlines, fines, or penalties for companies that don't switch.
Who counts as high risk for quantum attacks under the bill?
The bill points to critical infrastructure and digital infrastructure providers — think power, water, hospitals, and network operators. NIST decides the finer details.
Can organizations get federal grants to upgrade to quantum-safe encryption?
Possibly. NIST may create a grant program, but only after Congress appropriates money and NIST has issued post-quantum standards. Grants would cover reasonable upgrade costs.
How big would the post-quantum grants be?
The bill doesn't say. It lets NIST set a maximum amount and write the rules on eligibility, grant size, and duration.
Why prepare now if quantum computers can't break encryption yet?
Data stolen today can be stored and decrypted once quantum computers mature, and replacing encryption across large systems takes years. The bill aims to start that work early.
Does H.R. 3259 fund quantum cryptography research?
It adds post-quantum cryptography by name to the National Science Foundation's cybersecurity research agenda. It doesn't attach a new dollar amount.
Does H.R. 3259 have bipartisan support?
Yes. Rep. Haley Stevens (D-MI) introduced it with three Republican cosponsors, and the House Science Committee advanced it 35-0 in June 2025.
Based on H.R. 3259 bill text
Full Bill Text
Get notified when H.R. 3259 moves
Committee votes, floor action, cosponsor changes — straight to your inbox.
Bill alerts + Legisletter's monthly briefing. Unsubscribe anytime.
Science, Technology, Communications Bills
9 related bills we're tracking
AM Radio for Every Vehicle Act of 2025
Received in the Senate. Read twice. Placed on Senate Legislative Calendar under General Orders. Calendar No. 622.
Sep 16, 2026
Scientific Integrity Act
Referred to the House Committee on Science, Space, and Technology.
Feb 6, 2025
Kids Online Safety Act
Committee on Commerce, Science, and Transportation. Ordered to be reported with an amendment in the nature of a substitute favorably.
Aug 5, 2026
Sunshine Protection Act of 2025
Received in the Senate and Read twice and referred to the Committee on Commerce, Science, and Transportation.
Jul 15, 2026
GUARDRAILS Act
Referred to the Committee on Energy and Commerce, and in addition to the Committee on the Judiciary, for a period to be subsequently determined by the Speaker, in each case for consideration of such provisions as fall within the jurisdiction of the committee concerned.
Mar 20, 2026
Artificial Intelligence Civil Rights Act of 2025

Referred to the Committee on Energy and Commerce, and in addition to the Committee on Oversight and Government Reform, for a period to be subsequently determined by the Speaker, in each case for consideration of such provisions as fall within the jurisdiction of the committee concerned.
Dec 2, 2025
TAKE IT DOWN Act
Became Public Law No: 119-12.
May 19, 2025
States' Right to Regulate AI Act
Read twice and referred to the Committee on Commerce, Science, and Transportation.
Dec 17, 2025
ACERO Act

Received in the Senate and Read twice and referred to the Committee on Commerce, Science, and Transportation.
Feb 24, 2026
Trending Right Now
Bills gaining momentum across Congress
ASAP Act
Ordered to be Reported in the Nature of a Substitute by the Yeas and Nays: 40 - 0.
Sep 16, 2026
Federal Firearms Licensee Protection Act of 2025
Referred to the House Committee on the Judiciary.
Mar 3, 2025
Therapeutic Fraud Prevention Act of 2025
Referred to the House Committee on Energy and Commerce.
May 7, 2025
Tracking Science, Technology, Communications in Congress? Monitor bills, track cosponsor momentum, and launch advocacy campaigns — all from one advocacy platform.